The snapshot
An AI operating environment can coordinate labour, purchasing, clients and finances. The risk is not that it makes mistakes, but that the rest of the business acts on them before anyone notices. Whether AI can safely run a business depends less on the platform than on how authority, verification and accountability are designed around it.
- 5 actions
-
triggered by one unverified project status in the plasterboard scenario
- 36%
-
of 3,984 ClawHub skills scanned by Snyk contained prompt injection
- $5,000
-
net benefit left from an $80,000 saving once AI costs and rework are counted
Read this if you are
- running a business that is considering AI agents
- a director accountable for delegated decisions
- engaging a specialist to set up OpenClaw or a similar framework
Things to take away
- Agreement between agents is not verification. If several agents rely on the same data and assumptions, their agreement creates false confidence rather than an independent check.
- Set autonomy by consequence, not capability. Observing, recommending, preparing and executing carry different risks. A substantial purchase, a site safety decision or a contractual commitment needs a person.
- Measure cost per accepted build, not activity. Count the full cost of AI operations, oversight and rework against builds independently signed off at practical completion.
- Accountability cannot be delegated to software. WHS, director, privacy and consumer law obligations stay with the business, whoever or whatever made the decision.
- Own the operating capability, not just the installation. Documentation, company-held credentials and a second trained person inside the business belong in the specialist engagement from day one.
The promise of autonomous AI is changing the way business owners think about their operations. Instead of employing more people, adding management layers or investing in several disconnected software systems, what if a business could engage one specialist to configure an AI environment capable of coordinating much of its daily operations?
A prospective client recently presented a variation of this proposition. The construction business was considering bringing in an individual to establish OpenClaw as the foundation of an AI-powered operating environment. OpenClaw is an open-source agent framework, released under the MIT licence, that runs persistently on a machine the owner controls and acts through chat channels, scheduled tasks and a marketplace of community-built “skills” [1]. It was designed as a personal assistant. The proposal would stretch it a long way past that.
The ambition extended well beyond automating administrative tasks. AI would coordinate workers and trades, manage construction schedules, purchase materials, track the profitability of individual builds and communicate directly with customers about the progress of their projects. It would also monitor its own activities, with AI agents responsible for enforcing the guardrails governing other AI agents.
The commercial logic was compelling. Less administration. Faster decisions. Better coordination. Lower operating costs. More visibility across projects. Potentially, a business capable of scaling without increasing its workforce at the same rate.
There is nothing inherently unreasonable about pursuing these outcomes. Many are precisely the areas where intelligent automation could create substantial value. But the proposed approach raises a more consequential question. What happens when a business delegates not just individual tasks, but substantial operational authority, to an AI system configured and potentially maintained by a single person?
The decision is no longer simply about adopting AI. It is about who controls the business, how its decisions are verified and who remains accountable when something goes wrong.
Part 1 · The proposition
The attraction of an autonomous business
Construction is exactly the kind of fragmented, many-decision operation connected agents could improve.
Construction is a particularly good example of what connected AI systems could deliver. A single residential build involves dozens of decisions about labour, sequencing, materials, costs, subcontractors, inspections and client expectations. Multiply those across several simultaneous projects and the complexity compounds. Information is scattered across spreadsheets, accounting systems, emails, project management tools and the heads of individual employees.
AI offers the possibility of bringing these activities together. Imagine a system that continuously evaluates the progress of every build, identifies upcoming workforce requirements and checks whether materials will be available before the next stage begins. It could anticipate scheduling conflicts, identify emerging cost overruns and prepare accurate progress reports for clients. Rather than waiting for someone to discover a problem, it could surface issues earlier and recommend corrective action.
A successful implementation could improve several parts of the business at once.
-
Workers
Less time waiting for materials or instructions. -
Project managers
More attention on exceptions and quality. -
Customers
More consistent updates on progress. -
Owners
A clearer picture of project profitability. -
Overnight
Agents work outside business hours, so much of the coordination continues while the site is closed.
For a business on relatively narrow margins, even modest improvements in scheduling, procurement and cost control have a meaningful commercial impact. The opportunity is not simply to replace administrative work. It is to make the business more coordinated, responsive and economically efficient.
Yet these benefits depend on something easy to overlook. The system must make decisions using accurate information, understand the limits of its authority and recognise when it does not have sufficient evidence to act. That is where the complexity begins.
When one mistake becomes five
Agents that share the same data share the same errors. Their agreement is not a check.
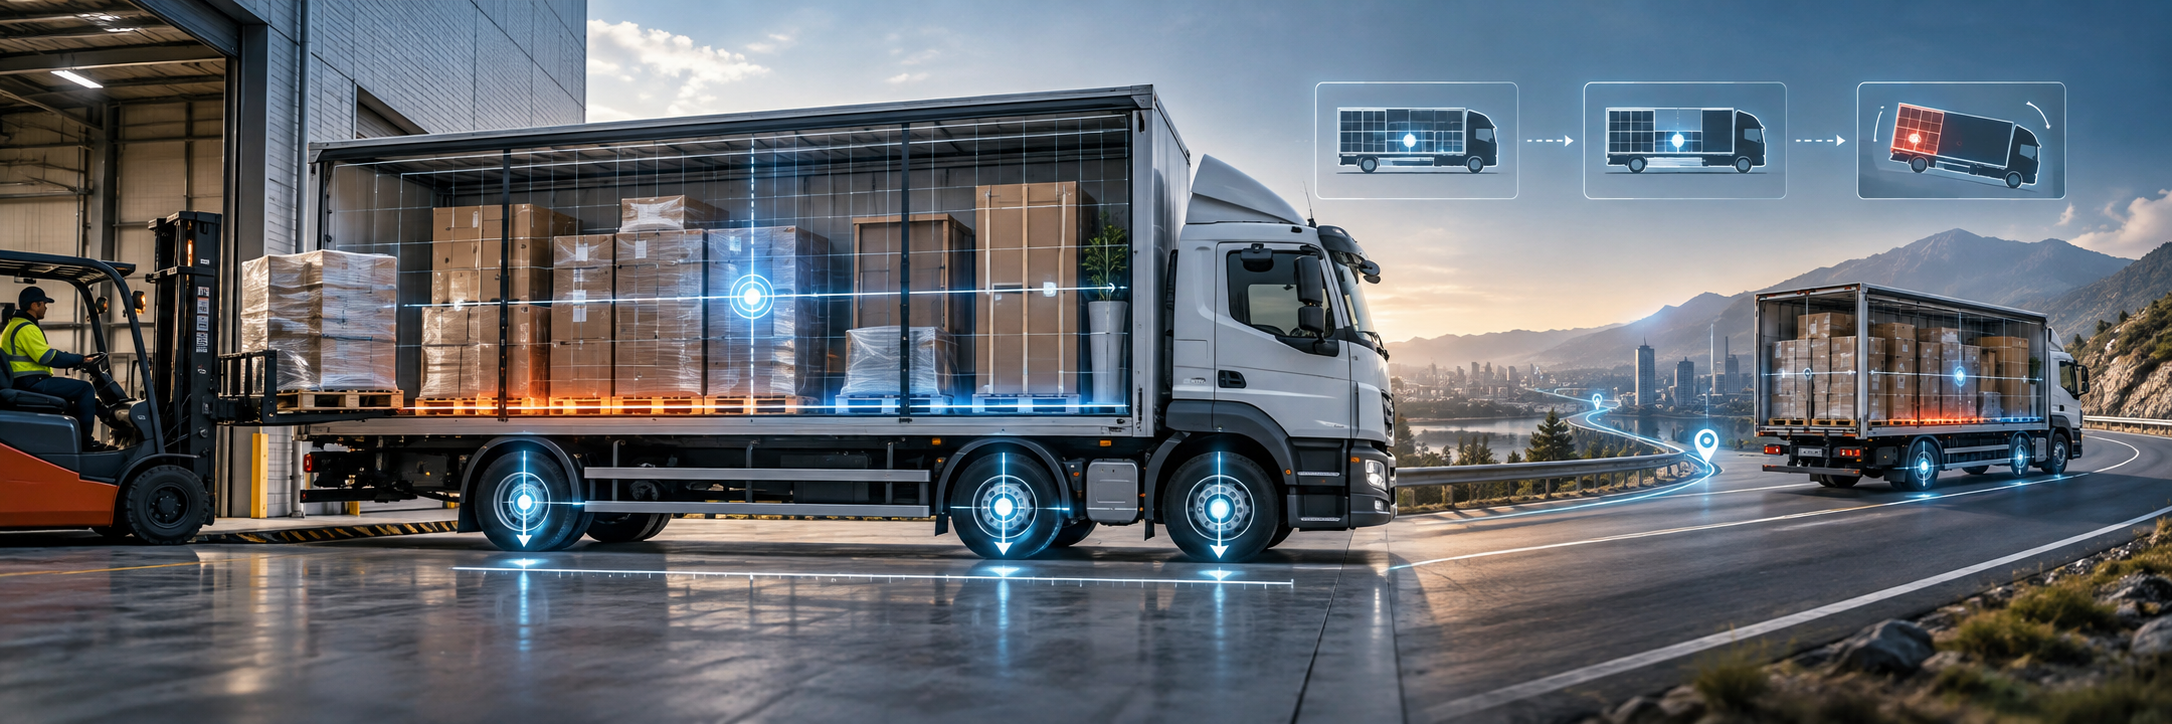
Consider an ordinary construction milestone. A project is approaching the stage when plasterboard installation can commence. An AI agent reviews the project management system and determines that electrical and plumbing rough-ins are complete. On that assessment, it schedules plasterers for the following week. A procurement agent orders materials. A communications agent tells the client the project is on schedule. A financial agent updates the projected cost and profitability of the build. An oversight agent reviews the activity, confirms that each action followed the prescribed workflow and records the process as compliant.
From the system’s perspective, everything worked. But suppose the original project status was wrong. A site inspection was incomplete, or an outstanding issue had not been recorded. The consequences now extend well beyond a single scheduling error. Workers arrive at a site that is not ready. Materials are delivered prematurely. The client has received an inaccurate progress report. The financial forecast reflects milestones that do not correspond with reality. And the AI responsible for monitoring the process has confirmed compliance, because every agent followed its instructions correctly.

Hypothetical scenario illustrating a common dependency and correlated-error risk, not an observed incident involving the prospective client.
This is one of the defining challenges of interconnected autonomous systems. In a conventional business, separate teams may catch inconsistencies because they work from different information sources, apply different expertise or independently challenge decisions. AI agents can provide similar checks, but that independence must be deliberately designed. If several agents depend on the same underlying data, assumptions or model behaviour, their apparent agreement creates false confidence.
The risk is not simply that AI makes a mistake. It is that the rest of the business begins acting on that mistake before anyone realises it exists. Greater automation increases the speed at which good decisions create value. It also increases the speed at which bad decisions create damage.
Can AI reliably police itself?
Checking that a process was followed is not the same as checking that the decision was right.
One of the more ambitious elements of the proposal was the intention for AI to monitor its own behaviour and enforce its own guardrails. At first glance this seems logical. If agents can perform operational tasks, why not create more agents to check their work?
There are real opportunities here. Monitoring agents can compare transactions against purchasing limits, flag unusual scheduling patterns, review communications for inconsistencies and identify activity outside established operating rules. They provide continuous oversight that would be difficult or expensive to reproduce manually.
But there is an important distinction between AI-assisted monitoring and independent governance. An agent checking another agent does not automatically establish an independent control. Both might rely on the same incorrect information, share assumptions about what success looks like, or interpret ambiguous instructions the same way. Worse, the system could be configured to assess whether a process was followed rather than whether the underlying decision was appropriate. There is a difference between checking that a purchase falls within an approved limit and confirming that the purchase is actually necessary. Verifying that a worker has been assigned to a project does not establish that the site is safe, the prerequisites are complete or the worker holds the right qualifications.
AI oversight therefore needs controls that do not depend exclusively on the AI system’s own judgement: independently enforced transaction limits, access restrictions, verified project milestones, external audits, human authorisation and the ability to suspend agent activity. OpenClaw’s own security guidance recognises the importance of such boundaries, including tool permissions, execution approvals, sandboxing and restrictions on access to sensitive systems [2].
- Process compliance Did the purchase fall within the approved limit? Was a worker assigned to the project?
- Decision quality Was the purchase necessary? Is the site safe, are the prerequisites complete, is the worker qualified?
The architectural principle is simple. AI can help monitor compliance, but it should not have unrestricted authority to define, modify, enforce and certify its own compliance controls.
Part 2 · Authority and cost
The difference between recommending and acting
Autonomy is a ladder. Each rung transfers more authority from people to software.
Autonomy is not a single capability. An AI system might observe what is happening, identify a problem, recommend a response, prepare an action or execute that action independently. Each level carries a different commercial and operational risk.
Five levels of autonomy · materials procurement
- Observe: timber needed in two weeks
- Recommend: propose quantities
- Prepare: draft the order for review
- Execute: place the order
- Verify: confirm delivery and cost
Each step to the right transfers more authority. From “Execute” onward the agent holds financial authority, and the consequences of a wrong decision land on the business.
Consider materials procurement. An agent identifying that timber will be needed in two weeks is providing useful information. Preparing a proposed order based on approved quantities and supplier pricing goes further, but still allows a purchasing manager to review it. Automatically placing the order introduces financial authority. If the order is wrong, the consequences include unnecessary expenditure, storage costs, delayed delivery of more important materials or disputes with suppliers.
The same distinction applies to workforce scheduling. Suggesting that electricians could attend a site next Tuesday is one thing. Directing workers to attend without an independently verified assessment of site readiness, qualifications and safety conditions is another. Client communications introduce their own complications. An AI system might accurately summarise verified progress. But if it begins making promises about completion dates, variations or costs, those communications shape contractual expectations and customer decisions.
These are not simply differences in technical capability. They represent different levels of authority being transferred from people to software. The most effective approach is not to maximise autonomy. It is to determine the appropriate level of autonomy for each activity, based on the consequences of an incorrect decision. A low-risk administrative task might be completed automatically. A substantial purchase, a site safety decision or a contractual commitment may require explicit human approval. This preserves much of the productivity benefit without assuming that every decision should be automated simply because automation is technically possible.
Cost reduction is likely to be one of the strongest arguments for this approach. If a business can reduce administrative workload, coordinate trades more efficiently and manage more projects with fewer people, the potential financial benefits are significant. But the comparison is more complicated than an AI subscription against an employee’s salary.
OpenClaw may be open source, but an operational environment built around it is not free. Model usage, infrastructure, system integrations, security, monitoring, maintenance, specialist support and independent verification all contribute to the total cost. There are also less obvious costs: correcting mistakes, reconciling inconsistent information and investigating automated decisions. The same problem is already visible in AI-assisted software development, where the number of features generated says nothing about their business value.
An AI system might coordinate hundreds of tasks each week, issue purchase orders and generate detailed reports. But if those activities introduce additional costs, delays or errors, more automation does not mean more productivity. The measure should be the economic outcome of the work. A useful starting point is how much the business spends to deliver a completed project that meets its contractual, quality and safety requirements:
The numerator captures more than materials and labour. It includes the allocable costs of AI operations, human oversight, defect correction, administration and the consequences of avoidable mistakes. An accepted build is one signed off at practical completion by the client, building surveyor or certifier, not one the AI system has marked as finished. Because projects vary in size and complexity, cost per accepted build belongs alongside project-level margins, schedule performance and quality measures rather than standing alone.
More importantly, the business should understand whether its AI investment is improving the profitability of each project. Suppose a builder spends $30,000 a year operating an AI environment. If the system saves $80,000 in verified administration and coordination costs with no loss of delivery quality, that is a meaningful improvement. But if it also creates $45,000 in rework, procurement mistakes and specialist intervention, the net benefit falls to $5,000.
A year (privacy adjusted)
AI saved $210,000. Running it and fixing its mistakes cost $198,000 of that.
- Spent operating the AI environment
- $150,000
- Lost to rework, procurement mistakes and specialist intervention
- $48,000
- Net benefit
- $12,000
Adjusted figures, not reported outcomes. The lesson holds regardless of the numbers.
The figures are hypothetical, but the lesson is not. The value of AI is not measured by the volume of activity it automates. It is measured by the improvement it delivers after the full cost of operating it is accounted for: margin, defects, schedule reliability, human intervention, procurement accuracy and customer outcomes. A business should be able to demonstrate not merely that its agents are working, but that their work is creating value.
Part 3 · Accountability and risk
Who is accountable when AI gets it wrong?
The obligations stay with the business. Delegating a task to software does not delegate the duty.
Accountability becomes pressing when AI makes operational decisions with financial, contractual or physical consequences. Who is responsible if an agent places an incorrect materials order? What happens when an automated scheduling decision contributes to an unsafe worksite? Who addresses a dispute when an AI-generated client update contains an inaccurate promise about completion dates or costs? And who answers for a financial agent that wrongly reports a project as profitable?
The fact that AI made these decisions does not remove the legal or commercial responsibilities of the organisation using it. In Australia, businesses remain subject to their contractual, employment, privacy, safety and corporate obligations. The precise position depends on the jurisdiction, the circumstances and the contracts, but the direction is consistent.
Four obligations that do not move
Work health and safety duties cannot be transferred. Under the model WHS laws adopted in every state and territory except Victoria, a duty holder cannot contract out of its duties, and any contractual term that attempts to transfer or reduce them is invalid [3]. Victoria’s Occupational Health and Safety Act 2004 takes the same position. Safe Work Australia’s July 2026 guidance on AI and digital technologies makes clear that these duties apply to the introduction of AI into a workplace in the same way as any other hazard [4]. New South Wales has gone further, passing amendments to its WHS Act that create an explicit duty around digital work systems that allocate work, including algorithms and AI; the amendments have not yet commenced, and Safe Work Australia has been asked to consider whether the model laws should follow [5]. An AI agent directing trades to a site is a digital work system allocating work.
Company directors retain oversight responsibilities. ASIC expects directors to understand their company’s finances, ask questions about delegated work and remain involved in the management of the business [6]. An organisation may delegate a task to software, but it cannot assume that doing so delegates away its underlying responsibilities.
Personal information raises its own obligations. A system managing workers, clients, contracts and project communications processes names, contact details, workforce records and commercially sensitive material. The Office of the Australian Information Commissioner advises organisations using AI to assess privacy and security risks, ensure appropriate human oversight and understand how personal information is collected, handled and disclosed. It also recommends, as best practice, that organisations not enter personal information into publicly available generative AI tools [7]. Many small builders sit below the Privacy Act’s $3 million turnover threshold and are currently exempt, though the government has proposed removing that exemption. The OAIC’s guidance still sets the standard a regulator, a client or an insurer will expect.
Client communications carry statutory exposure as well as contractual. An AI agent that tells a client a project is on schedule when it is not engages section 18 of the Australian Consumer Law on misleading or deceptive conduct, and for residential work, the domestic building legislation of the relevant state, which regulates variations and completion dates. That is a conduct problem, not a tone problem.
The organisation can automate the execution of work. It cannot automate away its accountability for the consequences.
None of these requirements is an obstacle to adopting AI. They are the environment in which businesses already operate. Autonomous agents simply make it necessary to reconsider how existing responsibilities are fulfilled. A company that gives an agent authority to purchase materials should define who authorises expenditure, what limits apply and how exceptions are handled. A company that automates scheduling should maintain verification of safety and operational requirements. A company that allows AI to communicate with clients should establish which statements the system is authorised to make, what must be verified and when a person steps in. And a company that relies on AI-generated financial reports must reconcile those figures with its accounting records. The organisation can automate the execution of work. It cannot automate away its accountability for the consequences.
The overlooked risk of depending on one specialist
Owning the servers is not owning the capability. Undocumented systems concentrate risk in one person.
The company was considering bringing in a single individual to configure and establish the AI operating environment. That might be a sensible way to begin. A talented specialist can create a working system quickly and at lower initial cost than an implementation team, and smaller organisations have always relied on capable individuals to build software, configure infrastructure and develop processes.
The risk arises when the specialist becomes the only person who understands how the system operates. Imagine the environment has been running for six months. Agents are coordinating projects, dealing with suppliers, updating customers and producing financial reports, and the company has become dependent on these workflows. Then the specialist becomes unavailable, or the commercial relationship ends. Who understands how the system was designed? Who knows which agents can execute transactions, where credentials are stored, how financial calculations are performed or why a particular model was selected? Who can tell whether the latest software update has affected the reliability of existing workflows? And if the system fails, who has the authority and knowledge to restore operations?
The company might own its OpenClaw installation, source code and servers. But ownership of technical components is not ownership of operational capability. An undocumented AI environment creates substantial dependence on the person who assembled it, and that dependence grows as automation spreads. Losing access to a single administrative tool is inconvenient. Losing confidence in a system responsible for scheduling, purchasing, customer communications and financial reporting could disrupt the entire business.
Open-source software reduces dependence on a proprietary vendor, but it does not eliminate dependence on a specialist, a model provider, undocumented configuration decisions or the project’s own direction. OpenClaw’s creator joined OpenAI in February 2026 and the project moved to an open-source foundation [8]; the framework the business builds on today is not governed by the people who governed it a year ago. Replacing several operational dependencies with one AI system does not necessarily reduce risk. It may simply concentrate it.
The solution is not to avoid engaging a specialist. It is to make knowledge transfer and continuity part of the engagement from the outset. Three measures do most of the work.
-
Documentation as a deliverable
Agents, permissions, data flows and model choices written down and owned by the company under the contract. -
Company-held credentials
API keys and administrative access held by the business, not the contractor. -
A second person before go-live
Someone inside the business walked through the configuration and able to operate it.
The organisation should remain capable of understanding, controlling and evolving its own operating environment.
Security becomes a business-wide concern
Software with legitimate access can be talked into illegitimate actions.
Traditional cybersecurity focuses on preventing unauthorised access to information and systems. Autonomous agents add another dimension: software that has legitimate access can be manipulated into taking inappropriate actions.
A procurement agent needs access to supplier emails, quotations, spreadsheets, purchasing systems and payment information. A scheduling agent needs employee details, project records and calendars. A communications agent processes documents, site reports and messages from external parties. These integrations create useful capabilities. They also create opportunities for malicious or misleading content to influence the agent’s behaviour.
The best-known example is prompt injection, in which instructions embedded in a document, message or webpage attempt to redirect an agent away from its authorised task. An agent reading a supplier quotation should treat that quotation as information to analyse, not as a source of authority over how it must behave. Without adequate controls, the distinction breaks down. OpenClaw’s documentation is candid on this point: it treats external content as untrusted, wraps it in warnings before passing it to the model, and states that even with strong system prompts, prompt injection is not solved. It recommends restricted tool access, execution approvals and sandboxing as the real controls, and its Docker-based sandboxing is not enabled by default [2].
For a business relying on one specialist to assemble the environment, the larger exposure may be the skills marketplace itself. OpenClaw agents gain capabilities through community-built skills, and the supply chain is poorly policed. Snyk’s February 2026 ToxicSkills study scanned 3,984 skills on the ClawHub registry and found prompt injection in 36% of them, and a separate analysis documented more than a thousand malicious skills that exfiltrated data [9]. A specialist installing third-party skills to connect an accounting package, email and a scheduling tool is installing exactly this risk.
When an autonomous system spans several business functions, compromised instructions can affect purchasing, files, customer communications or operational records, depending on the permissions granted. The response is not to prohibit integration. It is to ensure each agent has only the access and authority its assigned work requires. Security architecture must reflect the business responsibilities assigned to each agent, and controls with significant consequences should be enforced independently rather than relying on language-based instructions to a model.
Part 4 · The architecture
Building autonomy without surrendering control
Separate observing, analysing, recommending, executing and verifying. Set controls in proportion to consequence.
The most important architectural decision is not which AI platform to install. It is how the business distributes information, authority and accountability between AI systems and people. A well-designed environment separates five activities: observing what is happening, analysing information, recommending action, executing authorised tasks and verifying the outcome. These responsibilities should not automatically belong to the same agent.
- Observe
- Analyse
- Recommend
- Execute
- Verify
The business might allow AI to monitor milestones, forecast labour requirements and prepare supplier orders. But evidence of site readiness comes from a verified inspection, and purchases above an agreed threshold need approval from an authorised employee. Client updates can be generated automatically from verified project records, with exceptions escalated before messages are sent. Financial agents can continuously calculate projected margins, while reconciliation with the accounting system and approval of consequential adjustments remain independently controlled.
The aim is not to put a person in every loop. That would undermine the benefits of automation. It is to establish controls proportional to the impact of each decision.
Operating model · autonomy against independent control
| Function | AI autonomy | Independent control |
|---|---|---|
| Project monitoring | High | Verified source records and milestone evidence |
| Workforce scheduling | Conditional | Qualifications, availability, safety and site-readiness checks |
| Materials procurement | Conditional | Approved suppliers, spending limits and authorisation |
| Client progress updates | High for verified facts | Approval for contractual commitments or exceptions |
| Project profit and loss | High for analysis | Accounting reconciliation and financial oversight |
| AI compliance monitoring | High for detection | Independently enforced policies, audit and escalation |
| System configuration | Restricted | Change approval, testing and independent review |
These boundaries need not stay fixed. As the system demonstrates reliability, some activities can be granted more autonomy. Others will continue to require human authorisation because the consequences of an incorrect decision are too significant. The organisation should also retain the ability to disable individual agents, reverse transactions where feasible and continue essential operations if the AI environment becomes unavailable. Autonomy should be earned through demonstrated reliability, not granted because the technology makes it possible.
The competitive advantage is not the agent. It is the architecture.
Install the framework as a consequence of an operating-model decision, not as the starting point.
The business may be right to adopt OpenClaw. An open-source orchestration environment could be a flexible foundation for coordinating agents across existing systems. But the installation should be the consequence of an operating-model decision, not the starting point. Before committing substantial authority to AI, the business should be able to answer several questions.
Seven questions before you commit authority
-
Which decisions can safely be automated?
-
What information will agents rely on, and how is it verified?
-
Who approves consequential actions?
-
How are problems detected?
-
What happens when systems disagree?
-
Who can intervene?
-
How will the business measure whether automation is improving performance?
These questions matter because the technology will keep changing. New models, frameworks and agent capabilities will arrive; some will be better suited to particular tasks, others will offer better reliability, security or economics. A business that builds its operating model around the internals of one framework becomes constrained by it. A business that defines its processes, decision rights, data requirements and governance independently can adopt or replace AI components as they evolve. That is the distinction between implementing an AI tool and developing an AI operating capability. The tool performs work. The capability determines how work is initiated, coordinated, verified and controlled.
A sustainable implementation begins with a contained workflow, demonstrates measurable value and expands only once the supporting controls have been tested. For the construction business, that might mean using AI first to monitor progress, identify scheduling conflicts and prepare procurement recommendations. The next stage introduces limited execution authority for well-defined, low-risk activities. More consequential responsibilities follow only after the company has established reliable data, oversight and recovery mechanisms. This looks slower than handing an ambitious specialist broad access and asking them to automate everything. It is far less likely to reveal structural weaknesses only after the business has become dependent on the system.
There is an understandable attraction to the idea that one talented person, equipped with sufficiently capable AI, could operate systems that previously required a team. In some circumstances that may become commercially viable, and smaller organisations may gain access to capabilities once practical only for much larger ones. But reducing the number of people in a process does not remove the complexity of the process. Someone still decides what an acceptable outcome is, which information can be trusted, how competing priorities are resolved and what risk the organisation will accept. Someone remains accountable for the consequences.
AI can support those functions. It can surface information, evaluate options, identify inconsistencies and enforce clearly defined constraints. But the business needs an architecture that keeps those capabilities inside its own objectives, responsibilities and controls: one that is understandable, inspectable and adaptable, where a model can be replaced, an agent changed or another specialist engaged without losing control of operations.
The construction company considering OpenClaw may be pursuing exactly the right opportunity. It could build a more efficient operation, improve margins, reduce administration and deliver a better customer experience. But there are two ways that ambition could unfold.
- Dependent An interconnected collection of agents configured by someone whose decisions and assumptions are not fully understood.
- Governed An AI operating environment in which agents have defined responsibilities, constrained authority and independently verified outcomes.
Both could use the same models, the same framework and even the same specialist. The difference is the architecture around them.
The next competitive advantage will not come from having the most autonomous agents or the fewest employees. It will come from building a business that can move faster, operate more intelligently and scale without losing control. Because when AI begins running the business, the most important question is no longer what it can do. It is who decides what it should be allowed to do, and who remains accountable when it gets something wrong.
When AI begins running the business, the most important question is no longer what it can do. It is who decides what it should be allowed to do.
References and further reading
-
How to secure OpenClaw against prompt injection; OpenClaw security best practices Redwerk: https://redwerk.com/blog/openclaw-security-best-practices/
-
When technology becomes a WHS risk: NSW’s landmark Act spotlights digital work systems; NSW AI workplace safety laws Moore Australia: https://www.moore-australia.com.au/news/nsw-ai-workplace-safety-laws-digital-work-systems-2026/
-
The Executive’s Guide to OpenClaw; OpenClaw review Build to Launch: https://buildtolaunch.substack.com/p/openclaw-ai-agent-one-person-business